Security & Trust

Enterprise-grade security for your most sensitive data

Our security and privacy practices meet healthcare’s highest standards. With SOC 2 Type II controls, HIPAA compliance, and an audit trail of every interaction the agent makes, your patient data stays protected and under your control.

Assort security hub: approved workflows, logged and audited, your data stays yours, with SOC 2 and HIPAA badges

trusted by thousands of providers across 23+ Specialties and Fortune 20 Enterprises

The agent works inside your rules

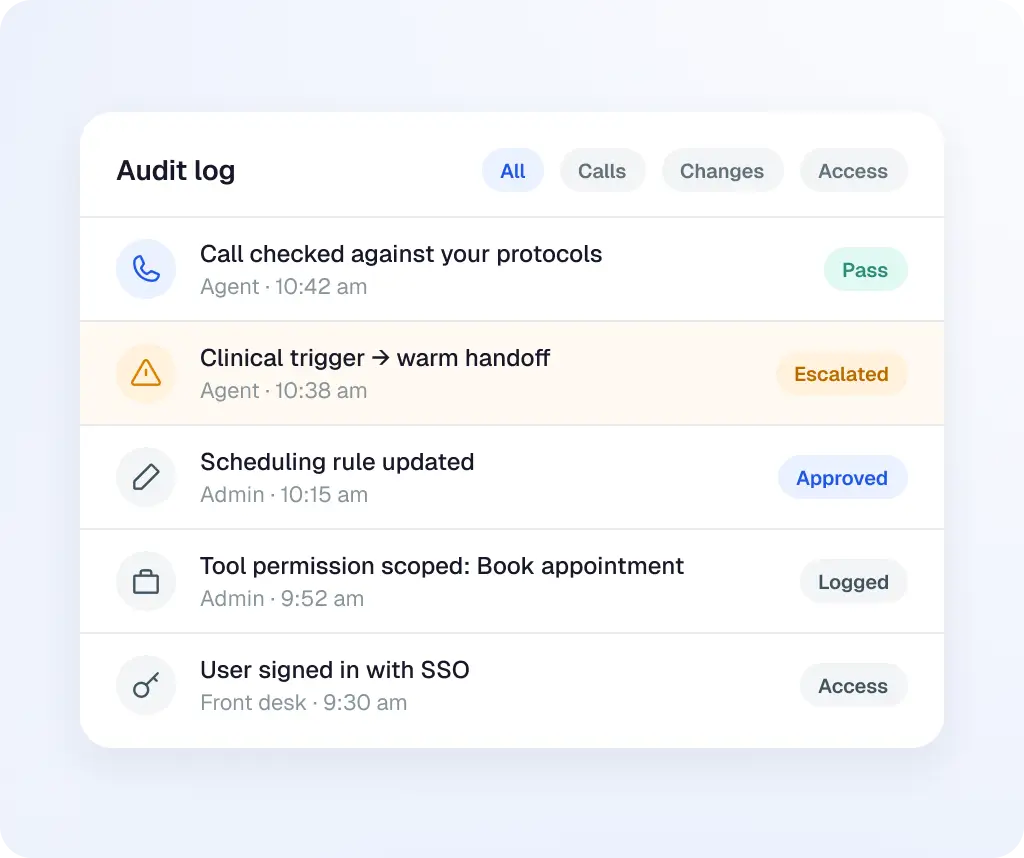
  • Every call is checked against your protocols. Assort automatically reviews agent behavior against your configured protocols.
  • Actions are limited to what you’ve configured. Each agent can only access the tools you’ve given permissions.
  • Built-in safety escalations that you define. When a patient says something you’ve flagged as clinical, the agent does a warm handoff to your team.
  • A full audit log. System activity, agent changes, access events, and operational workflows are tracked and logged.
Audit log showing calls checked against protocols, clinical escalations, approved rule changes, scoped tool permissions, and SSO access events
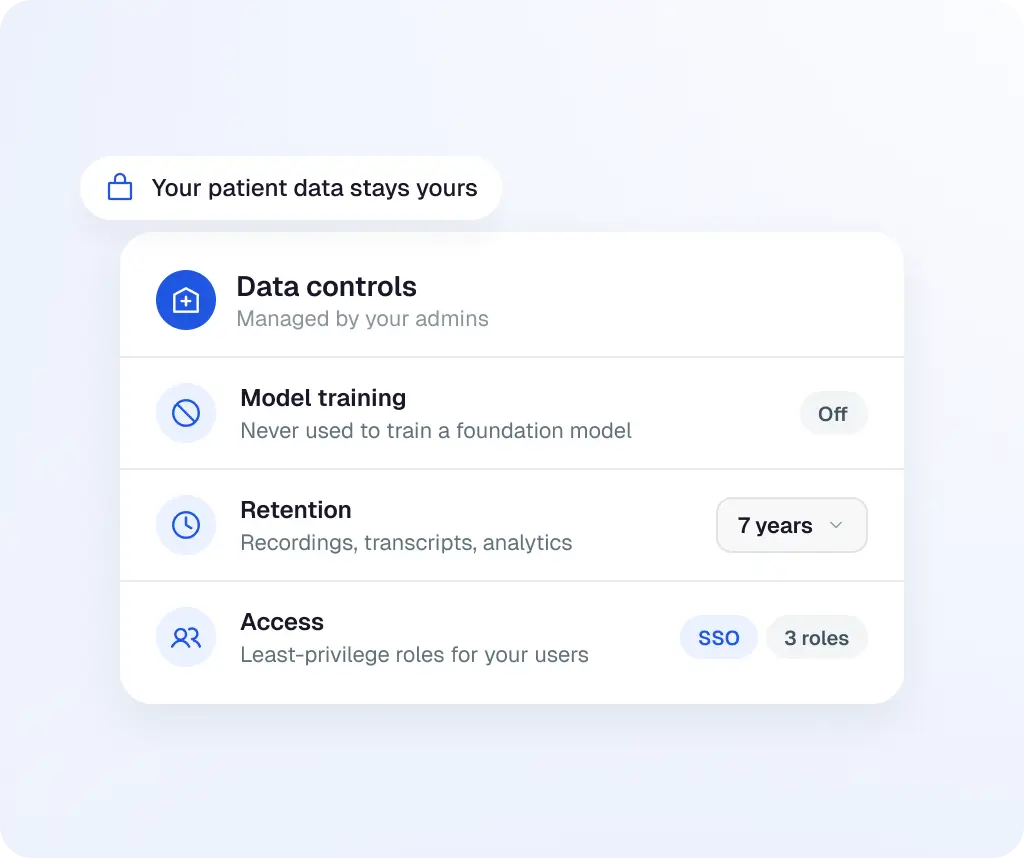
Data controls managed by your admins: model training off, configurable retention, and least-privilege access with SSO

Your patient data stays yours

  • No model training. We will never use your data to train a foundation model.
  • Retention on your terms. You set how long recordings, transcripts, and analytics are kept, to match your record policy.
  • Access your admins control. Manage least-privilege roles for your own users, with SSO sign-in.

Assort runs on audited controls

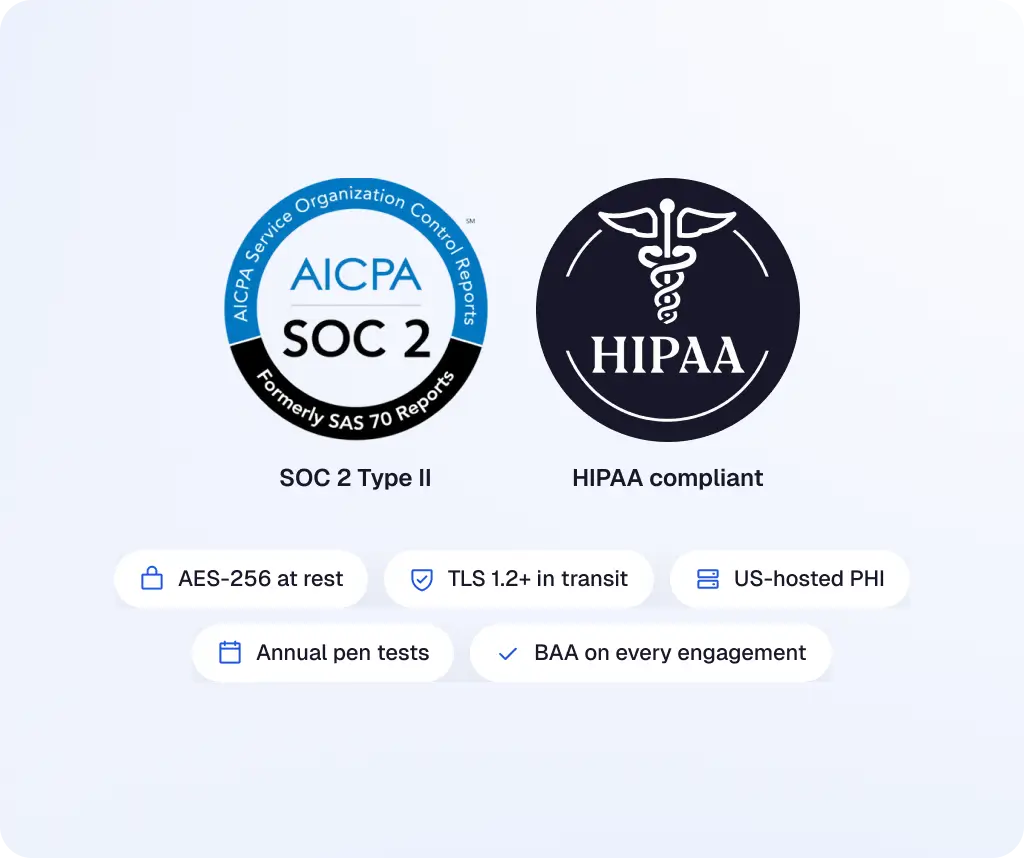
  • SOC 2 Type II and HIPAA. The SOC 2 Type II report and HIPAA attestation are available, and a BAA is signed on every engagement.
  • Encrypted, US-hosted PHI. PHI is encrypted with AES-256 at rest and TLS 1.2+ in transit, on US-based infrastructure.
  • Tested on a set cadence. Penetration tests, incident-response tests, and control self-assessments run annually.
  • Dedicated security team. Check current control status on the Trust Center, and get your questions answered by our security team.
SOC 2 Type II and HIPAA compliant badges with AES-256 at rest, TLS 1.2+ in transit, US-hosted PHI, annual pen tests, and BAA on every engagement

One shared security layer across Assort’s platform

Adding additional Assort products like Inbound, Self-Service, Outbound, Intake, Referrals, or Payments to an existing deployment is easy because it runs within one control environment.

Inbound

Voice AI that books on your protocols and improves with every call on the platform

Learn more →

Self-service

Every appointment type, bookable online

Learn more →

Outbound

Outreach that ends in a booked appointment

Learn more →

Referrals

Turn every referral into a booked appointment

Learn more →

Intake

Everything the visit needs, done before the patient arrives

Learn more →

Payments

Collect more patient balances, without a single staff call

Learn more →

Security controls your team can configure and audit

See how Assort protects patient data with HIPAA-compliant safeguards, audit logs, and controls your team configure.

Visit Trust Center

Frequently Asked Questions

Is Assort HIPAA compliant?

Yes. Assort is HIPAA compliant and can provide a HIPAA compliance attestation. Assort is also SOC 2 Type II audited, and the report and attestation are available under NDA.

Does Assort sign a BAA, and how is PHI protected?

Yes. A signed Business Associate Agreement is part of every customer engagement, and security commitments are documented in the customer agreement. PHI is hosted entirely on US-based infrastructure, encrypted at rest with AES-256 and in transit with TLS 1.2 or higher, with least-privilege role-based access control, SSO, and MFA governing every access path.

Is our patient data used to train AI models?

No. Customer data is never used to train third-party foundation models, and no-retention terms govern the model providers Assort uses.

How do we know what the AI agent actually did on a call?

Every interaction is logged and auditable. The platform records AI interactions, access events, and operational workflows, so any call can be reconstructed after the fact. No agent workflow change goes live without human review and customer sign-off.